A privileged password that remains unchanged for months is not simply an aging credential. It is an unmeasured exposure path to domain controllers, production databases, network devices, cloud tenants, and business-critical applications. If the account is shared, undocumented, or embedded in automation, that exposure can persist long after an employee leaves or an incident is closed.
Knowing how to rotate privileged passwords means more than setting an expiration policy. A defensible rotation program identifies every privileged account, controls who can retrieve credentials, changes them without disrupting dependent systems, and records proof that the process worked. The objective is clear: reduce the useful life of a stolen credential while maintaining operational continuity.
How to Rotate Privileged Passwords Without Causing Outages
Password rotation should be treated as an operational control, not a scheduled administrative task. The most common failure is changing a credential before understanding where it is used. A password may be stored in a service configuration, scheduled task, integration connector, deployment pipeline, database connection string, or emergency procedure. Rotating it blindly can interrupt production.
Start by creating an accurate inventory of privileged accounts. Include local and domain administrator accounts, root accounts, cloud administrator roles, database administrators, application service accounts, network device credentials, break-glass accounts, and vendor access accounts. The inventory should establish an owner, system scope, account type, business purpose, dependency status, and rotation requirement for each credential.
This step often exposes the real challenge. Organizations may have thousands of privileged accounts across legacy infrastructure, cloud platforms, SaaS administration portals, and industrial systems. Some accounts are active but unmanaged. Others have no known owner. These credentials should not enter a standard rotation schedule until ownership and dependencies are resolved. Rotating an unknown account may be safer than leaving it untouched, but disabling or changing it without validation can create a service interruption.
Classify accounts by risk and operational dependency
Not every credential needs the same rotation interval. A highly privileged account used to administer a production identity environment requires stronger controls than a local account on a low-risk test server. Risk-based policies allow security teams to focus control where compromise would have the greatest impact.
For example, privileged accounts with access to production, financial systems, sensitive health data, identity infrastructure, or security tooling may require rotation after every use or every checkout. Shared administrative accounts used for routine maintenance may rotate daily or weekly. Service accounts require a dependency-led schedule that reflects the application architecture and its ability to accept credential updates without interruption.
The interval matters, but context matters more. If a privileged password has been exposed, used from an untrusted endpoint, accessed by a departing administrator, or involved in an incident, rotate it immediately. Incident-driven rotation should not wait for the next scheduled cycle.
Establish a Controlled Rotation Workflow
A mature rotation workflow has defined stages: request or policy trigger, credential checkout, password change, dependency update, verification, and audit logging. Each stage should be controlled by policy and, wherever possible, automated through a privileged access management platform.
The password vault should generate and store unique, high-entropy credentials. Administrators should retrieve a credential only when authorized, ideally through a time-bound checkout process that records the user, target system, time of access, and reason for use. Once the session ends or the checkout period expires, the platform changes the password and updates the vault record.
Automation is valuable because it removes manual handling. A human administrator may forget a rotation date, reuse a password pattern, leave credentials in a spreadsheet, or fail to update a dependent system. PAM automation can execute approved change procedures consistently and produce the evidence auditors expect.
However, automation is not a substitute for validation. Every rotation workflow should confirm that the new credential works and that the old credential no longer provides access. If the process cannot validate the change, it should create an exception for review rather than reporting a successful rotation that did not occur.
Update dependencies before declaring success
Service accounts are where password rotation becomes technically demanding. These accounts often support unattended processes: application pools, middleware connectors, backup jobs, ETL processes, monitoring agents, and cloud integrations. A password change is incomplete until every authorized dependency has the updated credential.
Where supported, use credential providers, application-to-vault integrations, or managed identity alternatives to remove static passwords from application configurations. In cloud environments, workload identities and short-lived tokens can reduce the number of passwords that require rotation. In legacy environments, teams may need coordinated maintenance windows and scripted updates.
The right approach depends on the application. A customer-facing service with zero tolerance for downtime may need staged updates, redundant nodes, or a temporary dual-credential design. A noncritical batch process may support a simpler maintenance window. Document the dependency path and recovery procedure before the first rotation, not after a job fails overnight.
Protect Break-Glass Access Without Letting It Become Permanent Access
Emergency accounts need special handling. Organizations need a way to recover access if the identity provider, PAM platform, or network path is unavailable. But break-glass credentials are also highly attractive targets because they frequently bypass ordinary controls.
Store emergency credentials in a secured vault with restricted access, dual authorization where appropriate, and clear escalation procedures. Test the recovery process on a defined schedule. An untested emergency account is only a theory of resilience.
After any emergency use, rotate the credential immediately and review why it was needed. Repeated break-glass use usually points to a design or availability problem in the normal access path. Treat that pattern as an operational finding, not routine behavior.
Measure Rotation as a Control, Not a Checkbox
Security leaders need visibility into whether rotation is reducing risk in practice. Useful measures include the percentage of privileged accounts discovered and onboarded to PAM, rotation success rate, failed rotation count, credentials overdue for rotation, accounts without a confirmed owner, emergency access events, and the time required to revoke or rotate access after a personnel change.
Audit evidence should show more than a policy statement. It should demonstrate who accessed a privileged credential, whether access was approved, when the credential changed, whether the change was verified, and how exceptions were handled. This level of evidence supports compliance obligations while giving security operations a clearer picture of access risk.
Exception handling deserves discipline. Some systems cannot support automated rotation, and some legacy applications may require compensating controls while modernization is planned. Record the exception, assign an accountable owner, set an expiration date, and apply compensating controls such as session monitoring, network segmentation, tighter access approval, or increased review frequency. Permanent exceptions become unmanaged risk.
Build Rotation Into Privileged Access Operations
The strongest programs make password rotation part of the broader privileged access lifecycle. New accounts are onboarded to a vault before use. Access is granted through role-based policies and time-bound authorization. Sessions are monitored where risk warrants it. Credentials rotate after use or on schedule. Offboarding triggers immediate access removal and rotation for any shared or privileged accounts the individual could access.
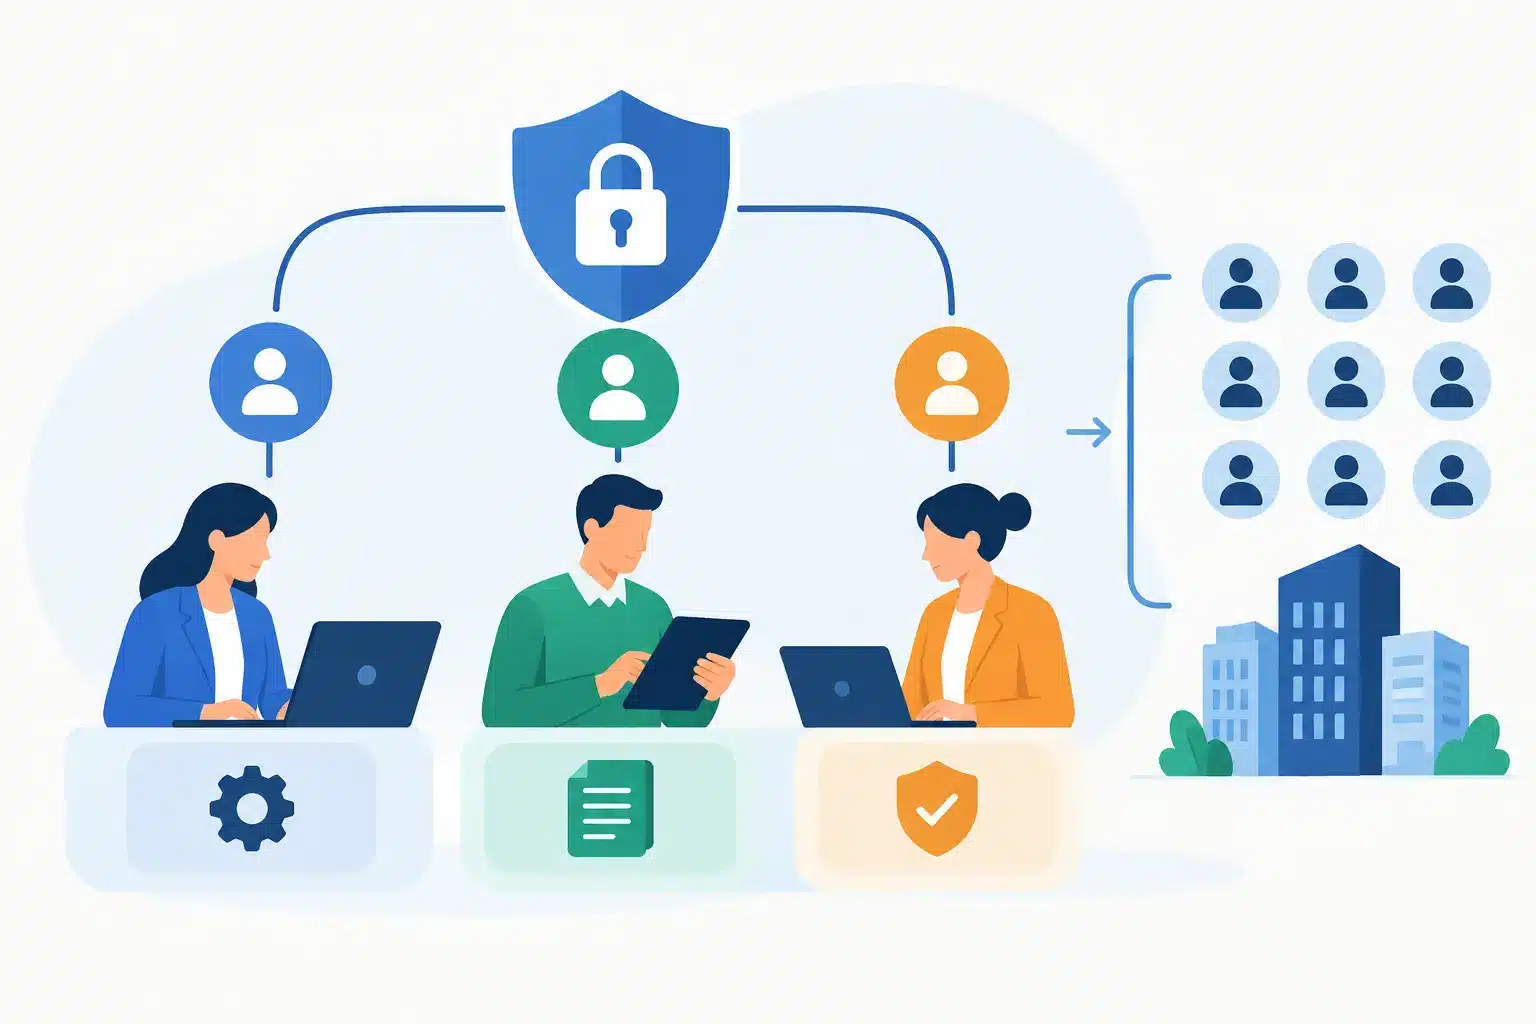
This operating model also requires coordination between identity, infrastructure, application, and security teams. Identity teams own policy and governance. Platform teams understand target systems. Application owners know dependencies. Security operations needs visibility into alerts and incidents. Without shared accountability, rotation becomes a fragmented task with predictable gaps.
For enterprises managing hybrid infrastructure, multiple PAM tools, or a large service-account estate, an assessment can establish the fastest path to control. IDENT1TY approaches privileged credential management as a sustained operating capability: inventory the exposure, define the control model, integrate the required systems, and measure results in production.
A privileged password should never be trusted simply because it is complex. Its real security value comes from controlled use, limited exposure, verified rotation, and the ability to prove who had access when it mattered.